Avoid Oracle Java Audits, save Millions.
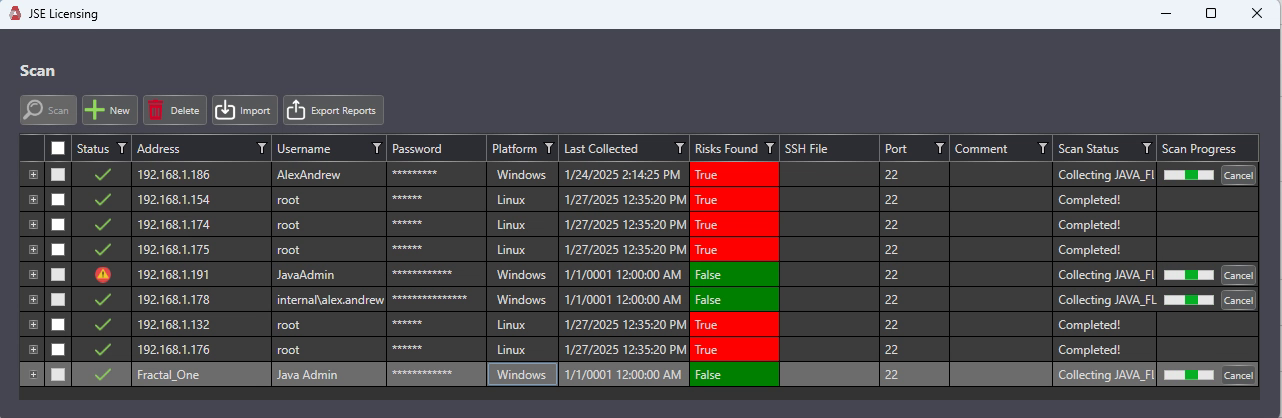
Using our Oracle-Verified tools and scripts deployed either directly or via SCCM we deliver an analyst reviewed compliance report. No agents on your network and no software to buy or maintain.
No agents. No cloud uploads. No third-party access.
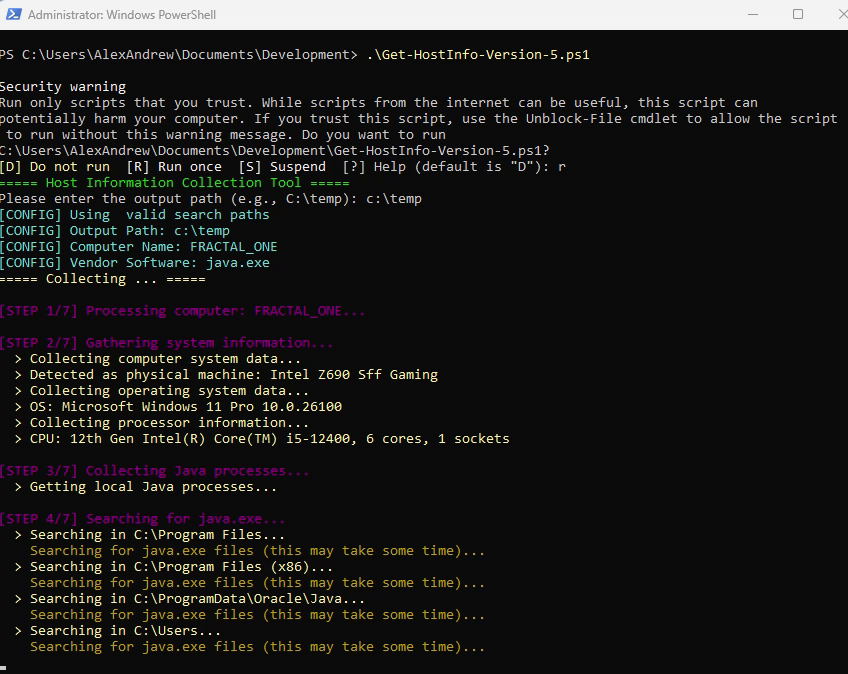
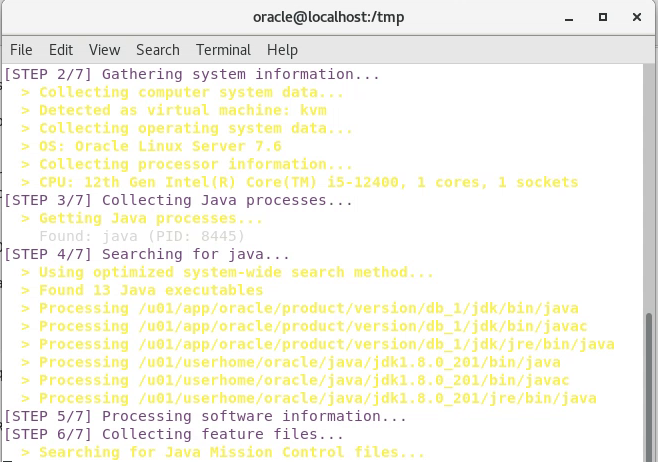
Collections can run as scripts — PowerShell for Windows and Bash for Linux — deployed via login scripts, SCCM, or your existing endpoint management tools. Every result is written straight to your own internal shared drive. Nothing is installed persistently, no data exfiltration, and no one outside your organisation sees the raw data before you choose to share it with us for review. Collections can also be run in tool directly using remote calls, CIM/PS/shell/SSH.
Your data on your network
No outbound connections, no cloud upload, no vendor portal. No data leakage risk because nothing leaves your infrastructure until you decide to share.
Oracle-verified, not generic SAM output
Our tool is verified by Oracle as part of the 3rd Party Tool Vendor (3PTV) Program — the collection method is checked by Oracle itself, and the report format is accepted in formal audit submissions.
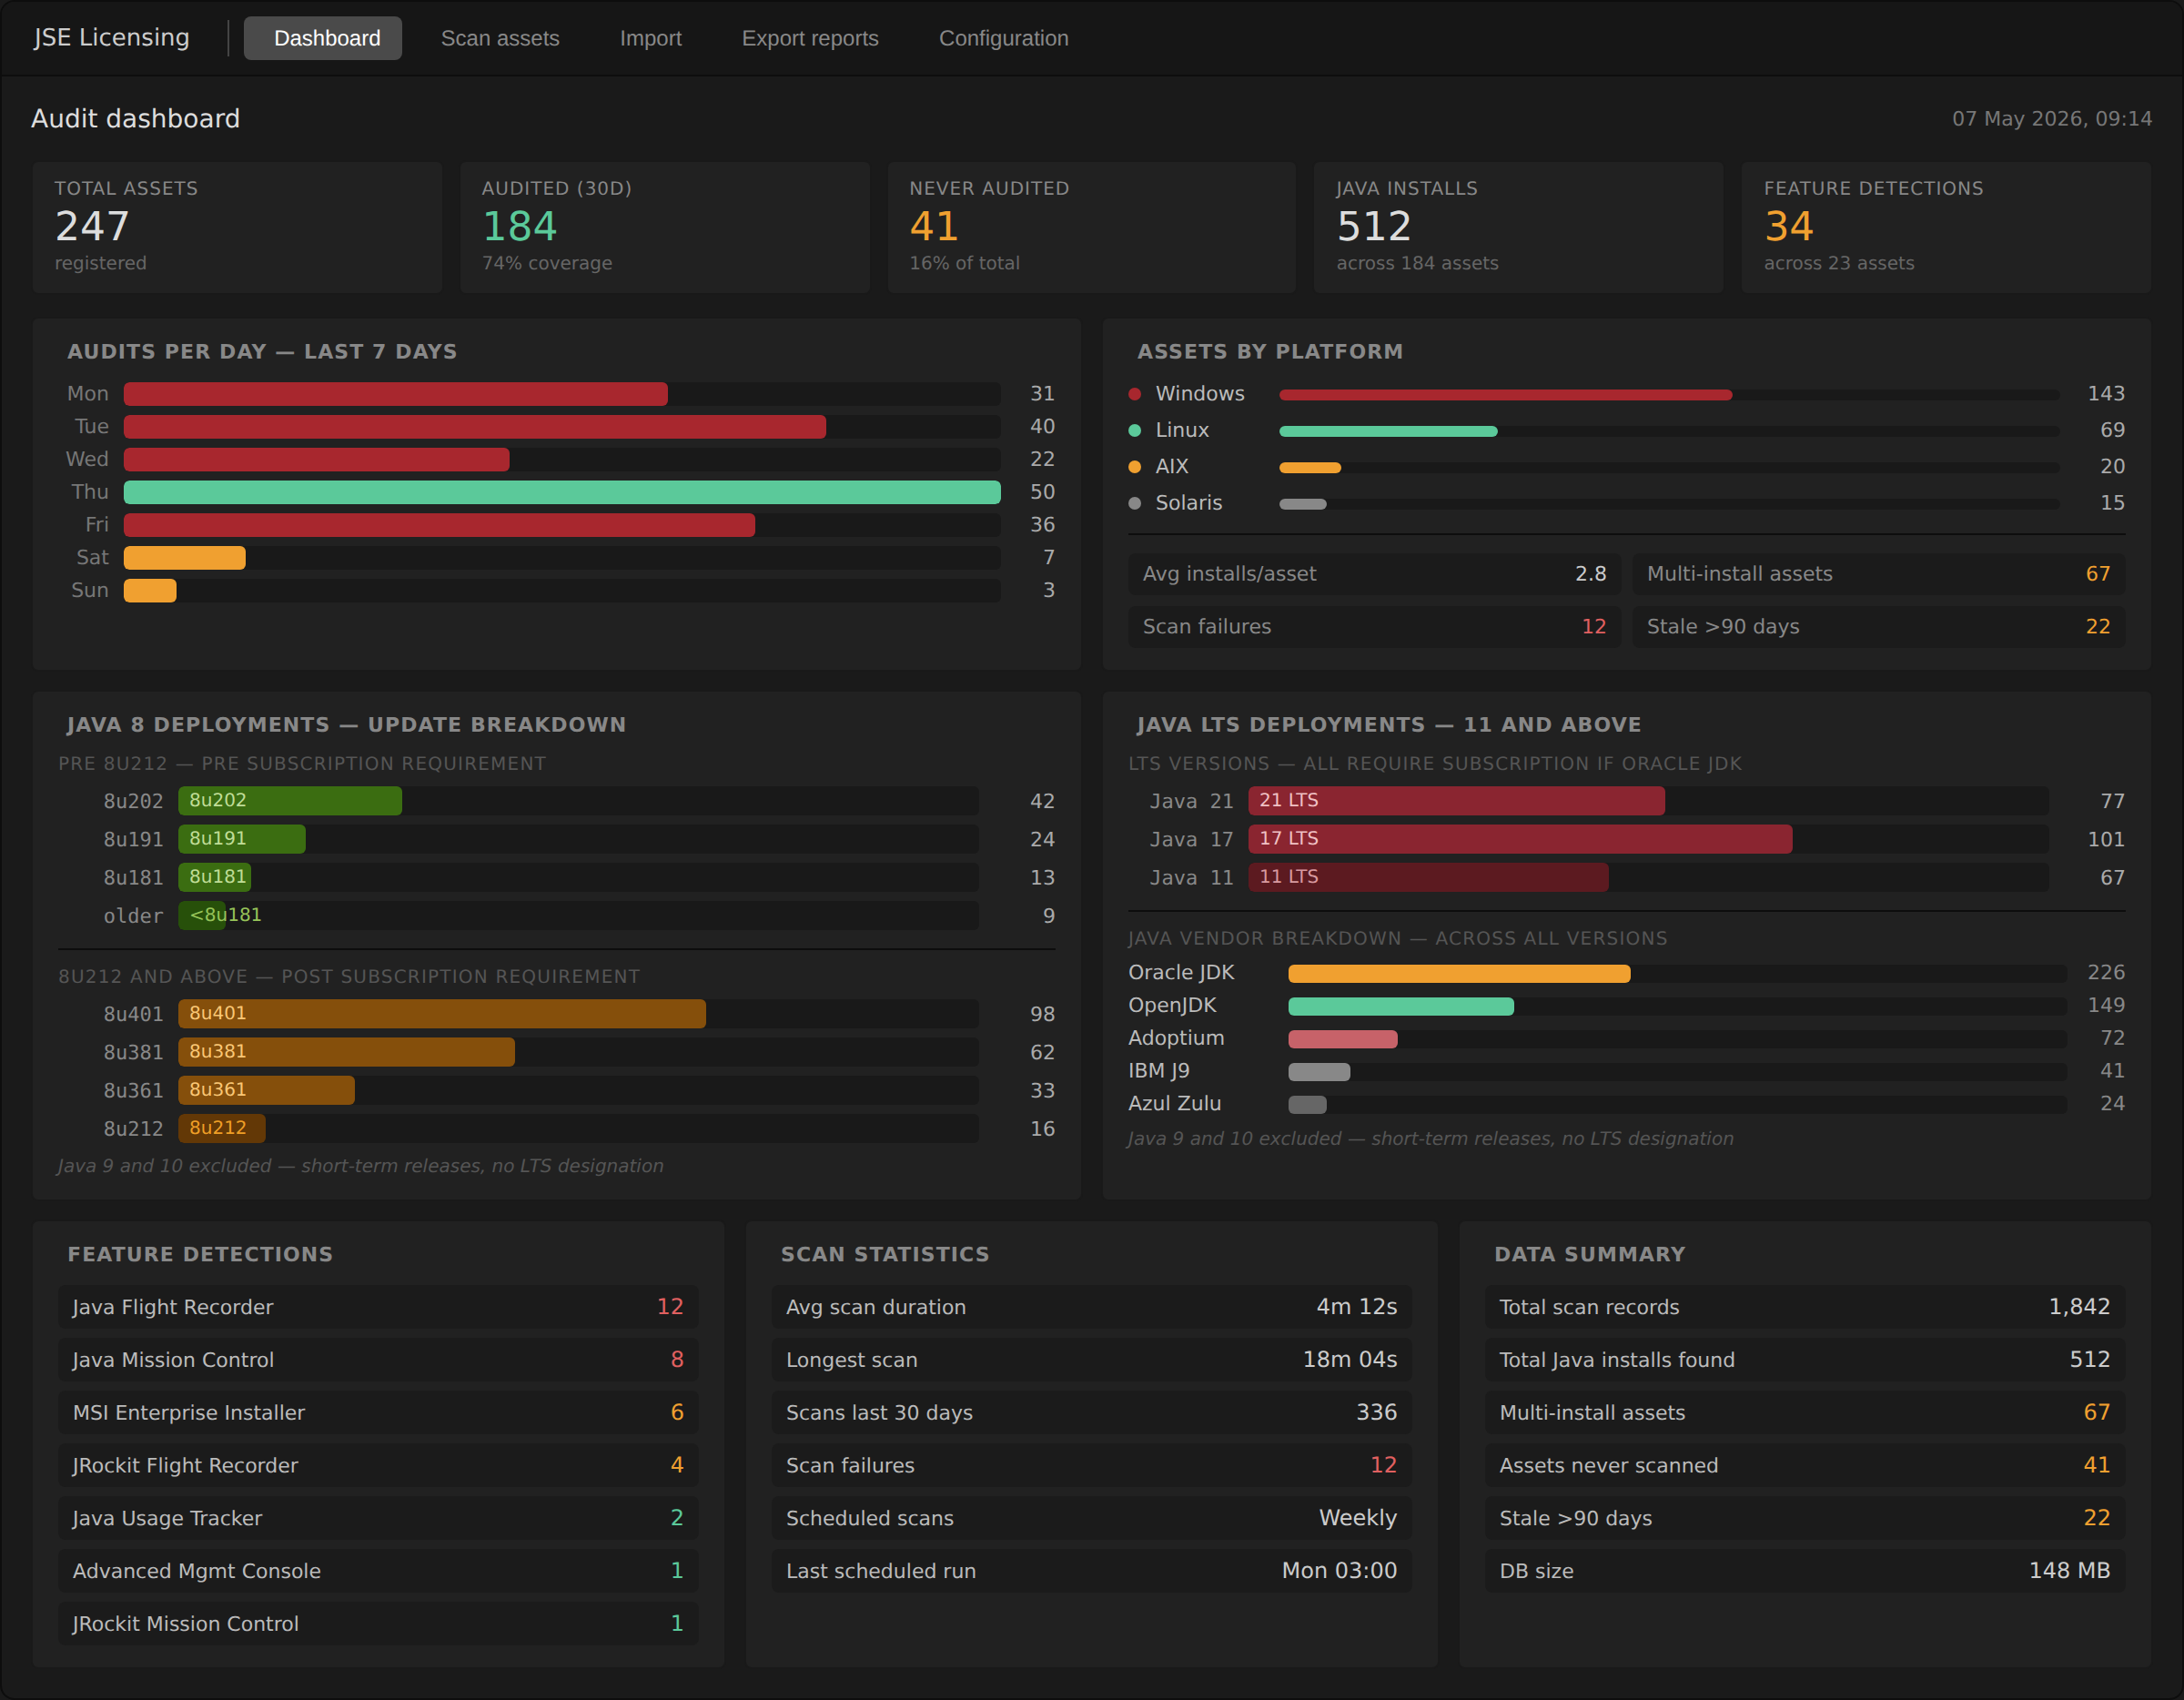
Built on CIM, not legacy WMI. Windows collection runs as PowerShell using CIM sessions over WinRM — the approach Microsoft now recommends for remote host management, in place of the older DCOM-based WMI calls that many networks block or flag. It's faster, works through modern firewall configurations.
15,000 Windows assets - full audit review in 14 days.
In our most recent enterprise engagement, a customer audited 15,000 Windows desktops and servers for Oracle Java usage in two weeks — without transmitting any audit data outside their internal network. The same approach scales for your entire organisation or single division, or a handful of assets you're specifically worried about.
Traditional SAM tools - implementation lag
All traditional SAM tools are Agent-based and use cloud-upload tools which can take months to deploy, our typical project takes less time than a tool vendor's implementation plan discussions.
Typical tooling
Agents expand who can access audit data. Uploads to vendor cloud systems raise data sovereignty and contractual exposure. Outbound telemetry increases your attack surface.
Our approach
No agents, no cloud upload, no external sharing. Data stays on your internal storage under your own access controls, start to finish.
Rapid Consulting, fixed cost and flexible reporting.
Fixed scope, flat fee, delivered as professional services — no software licence, and not a subscription.
Deploy
We walk your team through running the collection scripts or tooling — via login script, SCCM, or your endpoint management tool of choice — against your full estate, or just the assets you're worried about. It runs under your own change control; nothing is installed by us.
Review
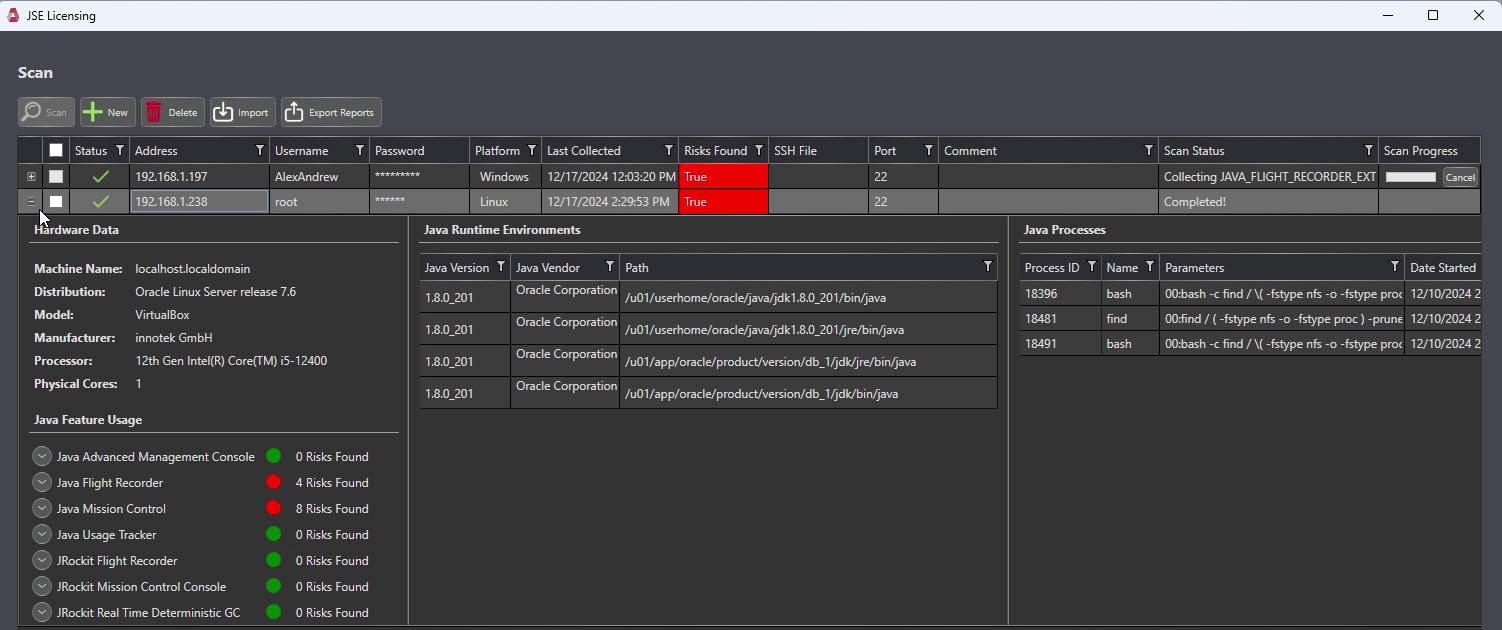
Your data comes back to us. The data is processed, and an initial quality report is issued.
Report
We walk through your compliance report and 3PTV statement together — we show you where you're exposed, potential ISV and Schedule A/B solutions, and what your options are.
Decide
The report is yours. If you want help acting on it — negotiation, migration planning, audit defence — that's a separate, scoped conversation.
What a review actually changes
UK Local Authority — facing a significant Oracle Java renewal uplift.
A full estate scan showed no requirement for widespread Java licensing — the authority's actual exposure was far narrower than Oracle's proposed renewal implied. They went into renewal negotiations with evidence, not guesswork, securing a significantly reduced cost versus the original uplift, and retained a limited level of licensing as a deliberate, risk-based choice given estate complexity — not because the data demanded it.
"Your approach was consistently supportive, accommodating and knowledgeable, which gave the team confidence in both the analysis and the decisions that followed … your expertise and the clarity of your recommendations enabled us to make an informed, evidence-based decision and achieve a far more cost-effective outcome."
Before you book
If you find Java on a few machines, does that mean we have to license everyone?
No. The report shows you where you already stand under Oracle's rules — it doesn't create the exposure, and it isn't sent to Oracle. Finding a handful of commercial JDK installs doesn't itself change your licensing position or obligate you to act a particular way. What you do next is entirely your call.
Does anything get installed on our network?
No. You run a script we provide, under your own change control, against whichever assets you choose. We never touch your infrastructure directly.
Is this a subscription or an ongoing commitment?
No — it's a fixed-scope, one-off engagement: two calls and a report. If you want a re-scan later, that's booked separately, on the same terms.
How is this priced?
Flat fee, agreed before you book, regardless of how many assets turn out to be running Java. We'll confirm the fee once we understand the rough size of your estate.
What's a "3PTV" report?
Output from an Oracle Verified 3rd Party Tool Vendor — a tool Oracle has checked and approved to produce accurate Oracle usage data.
What if we need help acting on the findings?
The Risk Review gives you the picture. If you need support with negotiation, migration, or audit defence afterwards, that's scoped and quoted separately as its own engagement.
Know your Java exposure, on your terms.
Answers you can act on.
 No agents · no cloud upload
25+ years Oracle licensing
Lime Software Ltd